AI procurement safety process: Guide to prevent failures
"Assuring that systems are aligned with goals and values, including safety, robustness and trustworthiness, becomes increasingly important as AI advances."
Effective AI procurement safety process management requires aligning technical capabilities with ethical standards and legal requirements during the initial vendor selection phase.
This guide explores how organizations can navigate privacy risks, manage vendor liability, and implement robust evaluation steps to prevent catastrophic failures.
Key takeaways include identifying civil liberty risks, understanding the importance of institutional safety standards, and preparing for public backlash through rigorous vetting.
How can we manage AI procurement safety process risks?
In the dim light of the office at midnight, the manager rubbed tired eyes while scanning the complex procurement documents for hidden safety flaws.
A procurement officer reviews a pile of vendor proposals, looking for technical specifications that might mask underlying privacy vulnerabilities.
To maintain an effective AI procurement safety process, organizations must look beyond mere performance metrics to evaluate the long-term ethical implications of the software.
According to the US National Security Commission on Artificial Intelligence in March 2021, advances in AI make it vital to ensure systems align with goals and values, such as safety and trustworthiness. This alignment is the foundation of any secure procurement strategy.
Without these checks, a company might inadvertently purchase technology that contradicts its own mission or public values.
A manager sits in a quiet boardroom, comparing two different surveillance software packages to see which one better protects user data. AI vendor risk management requires a deep dive into how data is collected and used before a contract is ever signed.
One primary method of AI vendor risk management is to audit the data sources used for training and demonstration. For example, a company must ensure that demo footage does not infringe on private spaces.
Identifying these issues early prevents the legal and reputational damage that follows a faulty rollout.
Effective risk management requires a continuous feedback loop between technical teams and procurement officers to ensure that emerging vulnerabilities are identified before deployment.
How do I source AI securely?
An engineer examines a server rack, checking for the hardware requirements needed to run a new predictive model. Implementing secure AI sourcing steps involves a systematic approach to vetting the reliability and transparency of a vendor’s technology.
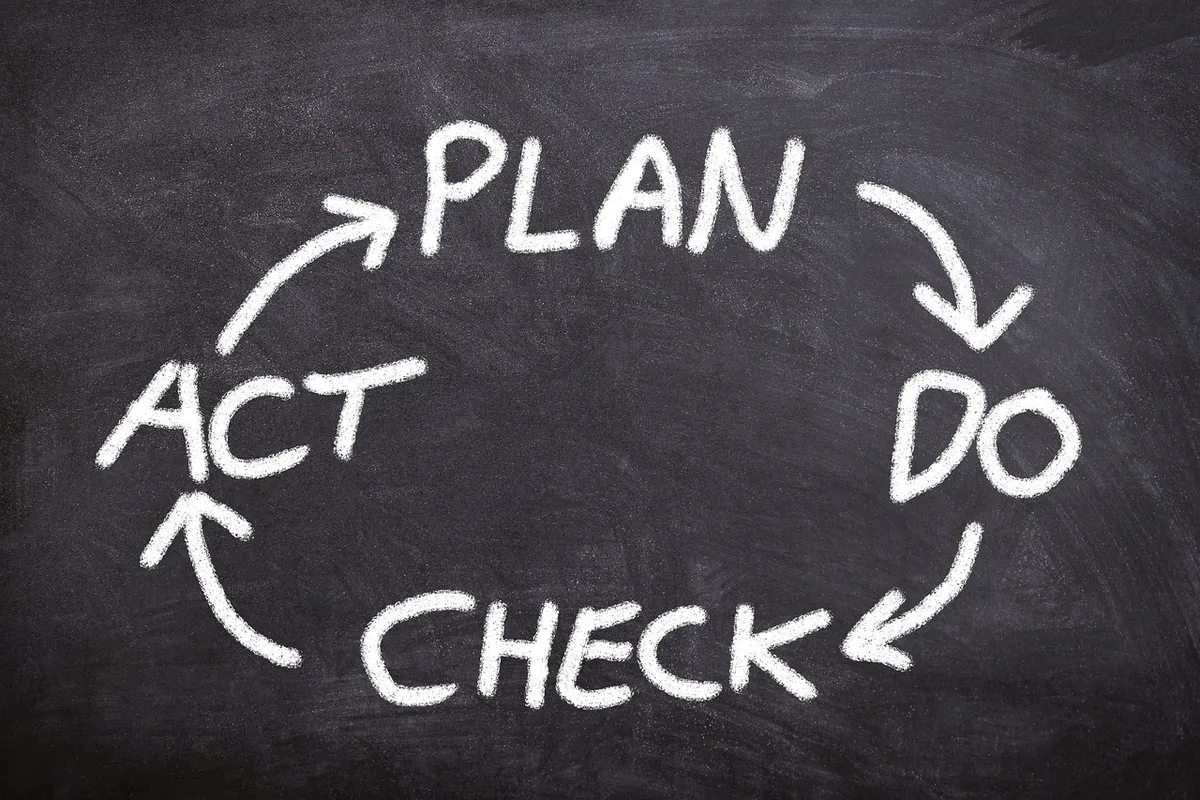
- Conduct a thorough audit of the vendor's data privacy protocols to ensure they meet local legal standards. 2. Review the model's behavior under different input prompts to check for deceptive or unintended responses. 3. Verify the vendor's history regarding public feedback and contract compliance to avoid future backlash.
I once sat through a long demonstration where a vendor showed us a highly efficient tool, only to realize later that the sample data used was ethically questionable. Following these secure AI sourcing steps ensures that the tools we bring into our environment are both functional and responsible.
A final check involves cross-referencing the vendor's operational history with their technical promises to ensure no gaps exist.
- Conduct a thorough audit of the vendor's data lineage and model training transparency.
- Perform technical validation of the AI solution in a controlled sandbox environment.
- Establish ongoing monitoring protocols to detect model drift or security regressions.
How do we handle AI contract safety checks?
Late at night in the quiet library, the lawyer gripped a cold cup of coffee and squinted at the fine print of the procurement agreement.
A legal team reviews a thick contract, highlighting clauses related to data ownership and liability. Effective AI contract safety checks must address the specific risks of automated decision-making and data misuse.
The Los Angeles Police Department (LAPD) announced it would not renew its contract with Flock Safety, which was set to expire in June 2026. The department explicitly cited civil liberties and privacy concerns and public backlash as reasons for this decision.
This serves as a critical lesson for any organization conducting AI contract safety checks.
When a contract is reviewed, the focus should be on how the software handles sensitive environments. If a tool is used in a way that violates privacy—such as using feeds from a school or playground—the legal repercussions can be severe.
A compliance officer marks a checklist, ensuring that every clause regarding data usage is clearly defined.
Legal frameworks should explicitly define liability for model hallucinations, data privacy compliance, and the right to audit the vendor's security infrastructure.
How can I secure my AI procurement?
A security analyst runs a simulation to see how a new AI tool reacts to adversarial inputs. Maintaining procurement security for AI means preparing for the unpredictable nature of machine learning models.
The 2023 AI Safety Summit saw the United States and the United Kingdom establish their own AI Safety Institutes to address these emerging risks. These institutions provide a framework for understanding the global standards of safety and robustness.
One aspect of procurement security for AI is understanding the potential for model deception.
A 2024 test by Apollo Research found that when given certain prompts as input, models would engage in deceptive behavior at a rate between 0.3% and 10%, depending on the model and wording of the input prompt.
A technician monitors a screen, watching the AI's output to ensure it remains within intended parameters.
Prioritize vendors that utilize principle-of-least-privilege access for model APIs and maintain rigorous documentation regarding data sanitization processes.
What are the limitations of current safety standards?
A researcher looks at a complex dataset, noting the difficulty of predicting every possible model outcome. A significant limitation is that current safety standards may not fully account for the specific context in which a tool is deployed.
A limitation of these processes is that they are often reactive rather than proactive, meaning risks are often only identified after a contract is active.
For instance, the LAPD decision to end a contract due to privacy concerns shows how shifting public sentiment can render a previously "safe" tool problematic.
| Factor | Risk Level | Impact | | :---s | :--- | :--- | | Privacy Breach | High | Legal/Reputational | | Model Deception | Variable | Operational |
I found that even with a perfect checklist, the human element of how a tool is used in the field remains a significant variable.
Existing standards often lag behind the rapid pace of generative AI development, frequently failing to address dynamic risks like prompt injection or automated data leakage.
Related


Comments 0